
Tech
Submit Your Flics: The Ultimate Guide to Secure File Sharing


In the digital age, file sharing is a common activity, whether for personal or business purposes. When you decide to submit your flics, it’s essential to ensure their safety and confidentiality. Secure file-sharing platforms have become a necessity for protecting sensitive information. This guide will explore why it’s important to submit your flics securely, and how you can do so while maintaining privacy and data integrity.
What Does It Mean to Submit Your Flics?
To submit your flics means to upload, share, or send files, such as images, videos, documents, or other digital content. Whether you’re sending personal photos to friends or sharing large work files, the method you use to submit your flics will determine how secure they are. In a world where data breaches are increasingly common, understanding how to protect your content is crucial.
Why Is Secure File Sharing Important When You Submit Your Flics?
When you submit your flics without proper security measures, you expose yourself to potential threats like hacking, identity theft, and data loss. Using secure file-sharing platforms ensures that your files are encrypted, making it nearly impossible for unauthorized parties to access your data. Whether you are sharing personal memories or sensitive business documents, secure platforms provide the necessary safeguards.
Core Features of Secure Platforms to Submit Your Flics
When choosing a file-sharing service to submit your flics, there are several key features you should look for. These include:
Encryption: This is crucial for protecting your files while they are being transferred or stored. It ensures that only the intended recipient can access the files.
Multi-factor Authentication (MFA): This adds another layer of protection, requiring more than just a password to access your account.
Secure Storage: Make sure your files are stored in a secure, encrypted environment to protect against data theft or loss.
With these features, you can be confident when you submit your flics, knowing that your files are safe and private.
How to Submit Your Flics Securely: Step-by-Step
To submit your flics securely, follow these simple steps:
Choose a secure file-sharing platform: Select a platform that offers encryption and multi-factor authentication. Platforms like Dropbox, Google Drive, and OneDrive are popular choices, but make sure to check their security features.
Encrypt your files: Even if the platform provides encryption, consider encrypting your files yourself for an added layer of protection before you submit your flics.
Set permissions carefully: Always limit access to your files. Only share with trusted recipients and give them the necessary permissions.
Verify recipient details: Double-check that you are sharing your flics with the correct recipient to prevent accidental exposure.
By following these steps, you ensure that your files remain secure when you submit your flics.
Common Risks When You Submit Your Flics Without Security
If you neglect to take security precautions when you submit your flics, you could face a variety of risks. These include:
Data interception: Without encryption, your files could be intercepted by hackers during transmission.
Unauthorized access: If your account is not secured properly, unauthorized users could gain access to your files.
Malware: Sharing files on unsecured platforms increases the risk of unknowingly distributing malware or viruses to others.
These risks highlight why it is critical to always secure your files before you submit your flics.
The Benefits of Using a Secure Platform to Submit Your Flics
The benefits of using a secure file-sharing platform to submit your flics are numerous:
Data protection: Encryption and secure transfer methods protect your data from unauthorized access.
Peace of mind: Knowing that your files are secure allows you to focus on other aspects of your work or personal life.
Collaboration: Secure platforms often have features that allow for easy collaboration while maintaining data integrity.
By using a secure platform, you can confidently submit your flics without worrying about data breaches or security vulnerabilities.
Choosing the Right Platform to Submit Your Flics
Selecting the right platform is crucial when you decide to submit your flics. Some factors to consider include:
Security features: Look for end-to-end encryption, MFA, and secure storage.
Ease of use: The platform should be easy to navigate, even for non-technical users.
Support: Ensure that the platform offers responsive customer support in case you encounter any issues.
Whether you’re submitting photos, videos, or other types of files, a reliable platform can make the process smooth and secure.
File Size Limitations and Speed When You Submit Your Flics
File size can sometimes be an issue when you submit your flics. Some platforms may have file size restrictions, which can limit your ability to share large files. Choose a platform that supports the size of the files you need to share and offers fast upload and download speeds to make the process more efficient.
Best Practices for Secure File Sharing
To further secure the process when you submit your flics, consider these best practices:
Use strong passwords: Make sure your file-sharing platform account is protected with a strong, unique password.
Enable MFA: This adds another layer of protection, reducing the risk of unauthorized access.
Avoid public Wi-Fi: When sharing sensitive files, try to avoid using public Wi-Fi networks to reduce the risk of hackers intercepting your files.
By adopting these practices, you ensure that your files stay secure when you submit your flics.
Legal and Ethical Considerations When You Submit Your Flics
When you submit your flics, especially sensitive data, it’s important to be aware of the legal and ethical considerations. Make sure you have the proper rights to share the content and are compliant with privacy laws such as GDPR or HIPAA, depending on the type of data you’re sharing. Ethical sharing involves respecting others’ privacy and using secure platforms to prevent unauthorized access to their data.
How to Track Files After You Submit Your Flics
Many file-sharing platforms offer tracking features that allow you to see who has accessed your files and when. This is especially useful in professional environments where file sharing is part of a larger project. By tracking your flics, you can ensure that they are being accessed by the right people.
Conclusion: Always Securely Submit Your Flics

Secure file sharing is a must in today’s digital age. By selecting the right platform and following best practices, you can ensure that your files are always protected when you submit your flics. Whether for personal use or business, safeguarding your data should always be a priority.
FAQs
Can I submit my flics securely using free file-sharing platforms?
Yes, many free platforms offer basic security features, but paid services typically offer stronger encryption and additional features.
Is it necessary to encrypt my files before submitting them?
While most platforms offer encryption, manually encrypting your files adds an extra layer of security.
How do I know if my files are secure after I submit my flics?
Most secure platforms offer tracking and monitoring features to verify that your files are being accessed by authorized users.
What should I do if I accidentally submit my flics to the wrong person?
Contact the platform’s support immediately to see if they can help revoke access or delete the file. You should also notify the recipient.
How can I avoid sending malware when I submit my flics?
Always scan your files with antivirus software before uploading or sending them to ensure they are clean.
Tech
Shaping the Future of Global Health: ‘Go Healthy with Taiwan 2026’ Unveils Top 20 Innovators from 62 Nations
Global campaign shatters records with 832 proposals, spotlighting breakthrough solutions in Smart Healthcare and Sports Tech.
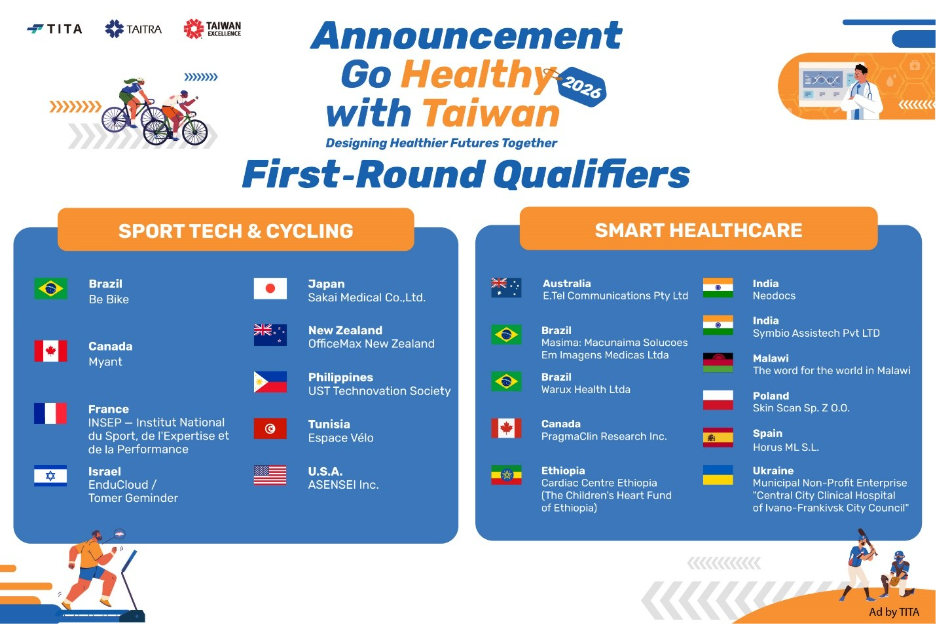
The 20 Semifinalists for the “2026 Go Healthy with Taiwan” competition.
The “Go Healthy with Taiwan 2026” global proposal campaign has selected 20 semifinalists from 832 proposals across 62 countries, with two more rounds of selection still to come. The 20 shortlisted teams hail from 16 countries worldwide, including Australia, Brazil, Canada, Ethiopia, France, India, Israel, Japan, Malawi, New Zealand, Philippines, Poland, Spain, Tunisia, Ukraine, and U.S.A., fully demonstrating strong international diversity and innovative energy.
This campaign is organized by the International Trade Administration (TITA), Ministry of Economic Affairs, Taiwan, and implemented by the Taiwan External Trade Development Council (TAITRA). This year’s campaign grew sharply: entries came from 62 countries and totaled 832, up 30% from last year’s 638 entries from 55 countries. The jump shows how many innovators worldwide now want to work with Taiwan’s health and sports technology companies.
The 20 teams work in two areas: 11 projects in Smart Healthcare, such as AI screening tools, remote patient monitoring, and better equipment for clinics, and 9 in Sport Tech & Cycling, such as injury prevention, rehabilitation, exercise for older adults, and safer cycling. The cohort features a rich variety of organization types, mostly companies (70%) with products already on the market, plus NGOs, government bodies, and universities that work directly with patients and communities. They vary in size too: small and mid-sized firms make up 45% of the list, with large companies making up the rest. Whatever the technology, the teams are chasing four goals: finding illness earlier, making care affordable in rural and under-served areas, helping people move safely, and helping older adults stay independent.
Here is how the 20 teams line up against those four goals:
Finding illness earlier
- Horus ML S.L. (Spain) — AI that screens for heart disease risk.
- Masima: Macunaima Solucoes Em Imagens Medicas Ltda (Brazil) — AI-driven quantitative brain CT and MRI analysis developed with Taiwanese digital health platforms.
- Myant (Canada) — smart clothing that tracks vital signs continuously.
- Neodocs (India) — reads a urine test strip with a smartphone to screen for kidney disease in 30 seconds.
- Skin Scan Sp. Z O.O. (Poland) — AI that screens skin lesions.
Making care affordable in rural and under-served areas
- Cardiac Centre Ethiopia Cardiac Centre Ethiopia (The Children’s Heart Fund of Ethiopia) (Ethiopia) — offline-first cardiovascular and NCD clinical decision support for grassroots health centers.
- Municipal Non-Profit Enterprise “Central City Clinical Hospital of Ivano-Frankivsk City Council” (Ukraine) — rebuilding high-standard operating rooms with Taiwanese equipment.
- PragmaClin Research Inc. (Canada) — 3D cameras and AI that measure Parkinson’s symptoms, bringing assessment to rural patients.
- The word for the world in Malawi (Malawi) — IoT water sensors and hydroponic systems to secure safe drinking water and combat child malnutrition.
- Warux Health Ltda (Brazil) — Taiwan’s contactless vital-sign AI built into WhatsApp care services.
Helping people move safely and avoid injury
- ASENSEI Inc. (U.S.A.) — real-time movement analysis for gyms and fitness coaches.
- Be Bike (Brazil) — smart sensors on delivery riders’ e-bikes to cut downtime and fatigue.
- Espace Vélo (Tunisia) — Edge AI in a smart health mobility platform.
- INSEP – Institut National du Sport, de l’Expertise et de la Performance (France) — an injury prevention platform for athletes.
- OfficeMax New Zealand (New Zealand) — smart e-mobility packages for corporate green commuting and employee wellness.
Helping older adults stay active and independent
- E.Tel Communications Pty Ltd (Australia) — wandering detection for people with dementia.
- EnduCloud / Tomer Geminder (Israel) — exercise prescriptions for older adults.
- Sakai Medical Co.,Ltd. (Japan) — Taiwanese equipment that helps older adults live independently.
- Symbio Assistech Pvt LTD (India) — a cabin-sized folding wheelchair built with Taiwanese precision parts.
- UST Technovation Society (Philippines) — smart e-bikes and trainers with biometric monitoring for cardiac and chronic disease rehabilitation.
Because each proposal is built around Taiwanese products and technologies, these ideas also have a clear path from prototype to wide, everyday use.
The 20 semifinalist teams will now work one-on-one with industry experts to improve their proposals. The campaign is scheduled to officially announce the final 6 shortlisted teams in early November. Those 6 teams will be invited to Taiwan to pitch in person. Three of them will be chosen as winners, and each will receive US$30,000. Expectations are high as to who will take home the top honors—stay tuned! For comprehensive details regarding all 20 shortlisted proposals, please visit our official website: https://gohealthy.taiwanexcellence.org/
About the Go Healthy with Taiwan Campaign
“Go Healthy with Taiwan” is a global proposal campaign aimed at connecting global innovators, institutions, and organizations with Taiwan’s health and wellness industry to jointly develop new solutions for health and wellbeing.
The 2026 campaign, themed “Designing Healthier Futures Together,” focuses on Cycling, Fitness & Sports Technology, and Smart Healthcare. Participants are encouraged to incorporate Taiwanese products, technologies, services, or business models into their proposals. Selected participants will receive expert mentorship and have the opportunity to engage with Taiwan’s industry ecosystem.
According to Google Cloud, misconfigurations remain the main risk when it comes to running workloads in production on Google Cloud Platform (GCP). In 2025 alone, businesses across various industries faced financial loss of over 10.22 million dollars due to a data breach. This is why securing GCP environments should be treated as an ongoing job and done with diligence.
In this article, we’ll break down how to protect GCP workloads in production and keep your systems safe without turning your workflow upside down. Let’s get right into it.
Build Security on a Strong Identity Foundation
GCP uses Identity and Access Management (IAM) to decide who can do what. While this sounds simple and pretty obvious, this is where most teams trip up. Instead of giving specific roles to each user, group, or service account, they hand out broad roles like Project Editor or similar and end up with too many users having permissions that they don’t need.
Don’t make that mistake. Stick to the principle of least privilege.
- Give users and services only the access they really need, even if that means spending more time on setup.
- Make sure to regularly run the IAM Policy Analyzer to find out what users have what access and how many of them they use, so you can further tighten access control.
- Avoid relying on service account keys.
Once widely popular, these service account keys have become easy prey for cyber attackers who steal them from phishing and infected devices. Instead, opt for Workload Identity Federation and multi-factor authentication.
These simple precautions can help prevent breaches and give you more organized access control.
Segment Your Network Like a Pro
Your network is your first line of defense. If protected, no attacker will be able to get in. This is why segmentation should be given particular attention. Use Virtual Private Clouds (VPCs) for different environments like development, staging, testing, and production workloads. This way, if attackers somehow get into one area, they won’t be able to move across other environments.
Next up, give your attention to VPC Firewalls. Oftentimes, they are set up to allow traffic on all ports, which exposes sensitive data to breaches. Make sure to tweak the setup, ensuring they only allow traffic that is necessary.
For highly sensitive data, you can go a step further and add VPC Service Controls. This will let you draw a perimeter across specific Google-managed services (Cloud Storage, BigQuery, etc.) so that data can only move to approved networks. For example, if someone gains login credentials, they won’t be able to copy data out of that designated VPC security perimeter.
Use Built-In GCP Security Tools Early
Many teams make the mistake of waiting too long before finally deciding to set up security tools. And while GCP offers a solid suite of built-in services for building applications, the intricacies that come with it often limit flexibility and introduce unnecessary challenges. This is why opting for GCP security tools from the outset is often the best decision for many organizations.
Encrypt Data
Data encryption is a vital step in securing sensitive production data. The good news is, GCP automatically encrypts data at rest with Google-managed keys, but as an extra step, especially for regulated industries like healthcare, finance, etc., you can use Customer-Managed Encryption Keys via Cloud KMS on services like Compute Engine disks or BigQuery tables.
To eliminate the risk of possible key theft, ensure that:
- You store these keys along with your important assets, such as personal databases or financial records.
- You run automatic rotation at least once every 90 days.
For application secrets like API keys, certificates, and passwords, use Secret Manager instead of hard-coding them. Google guidance emphasizes the importance of storing “keys, passwords, certificates, and other sensitive data” in managed services, not in code.
Set up tight IAM policies on these secrets. They should only be accessible to developers at runtime and a few admins who’ve been granted access to rotate or delete them. This will add a strong layer of protection to your environment and reduce the chance of misuse or data leaks.
Harden Your Computer Workloads
Lock down the machines and containers themselves. For Virtual Machines (VMs), always use Shielded VMs, which are easy to enable simply by clicking the box on creation. This will enforce secure boot and firmware verification to prevent low-level compromise.
Keep all operating systems and container images patched. If not done already, make sure to enable OS patching or vulnerability scanning. For GKE containers, use tools like Container Analysis or Binary Authorization to scan container images for CVEs and only allow deployment of images signed by your CI/CD pipeline.
Finally, make it a rule to run only essential services on each host and avoid installing all services just in case. Containers and VMs should be treated as single-purpose workloads. For example, if you’re using Kubernetes, don’t run your own SSH daemon in pods.
Continuously Monitor, Audit, and Respond
You can’t fix what you don’t see. This is why it’s vital to continuously monitor what’s happening in your system and make adjustments. Enable Cloud Audit Logs for all admin and data access, and send these logs to a central logging project or SIEM as per Google recommendations. This will help your team spot any sudden new grants and block them from breaking into the workload.
Keep tabs on things like:
- Failed login attempts;
- Unusual traffic spikes;
- Changes in IAM policies.
Use Security Command Center (SCC) Premium to compile a list of all security findings from multiple resources and receive reports on threat detection events. Google stresses that this tool is particularly good at catching broadening of access and permissions, which is often the major reason that leads to breaches.
Make sure to set up alerts for unusual events. Cloud logging can trigger alerts on patterns like IAM roles being changed outside the usual change window or unusually large GCS object reads. Your audits should be thorough and regular.
Final Thoughts
To bring it to the chase, securing GCP workloads in production isn’t a “done-and-forget-it” job. It’s an ongoing work that requires constant attention and adjustments. However, if you combine the right tools, approach, and tight control over everything that happens in your system, the new habit of keeping your system safe can save you millions of dollars that could be lost due to malicious attacks.
We translated 19 brutal MIL-STD-810H lab tests into real-world reliability for job sites. Here’s what it means for your gear.
See how RETEVIS Industrial Two Way Radios like RETEVIS RB48 series prove their reliability. We break down the extreme MIL-STD-810H military testing they pass and what that means for durability on your construction site or factory floor.
The claim of “military-grade” gets tossed around a lot in consumer tech, often with little to show for it. But for companies building tools that people’s safety and livelihoods depend on, that claim needs to be backed by a verifiable pedigree. For RETEVIS Industrial Two Way Radios, that proof comes in the form of a 47-page, third-party test report. Their RETEVIS RB48 and RB648 series radios have been subjected to—and passed—the full gamut of 19 environmental tests outlined in the U.S. Department of Defense’s MIL-STD-810H standard.
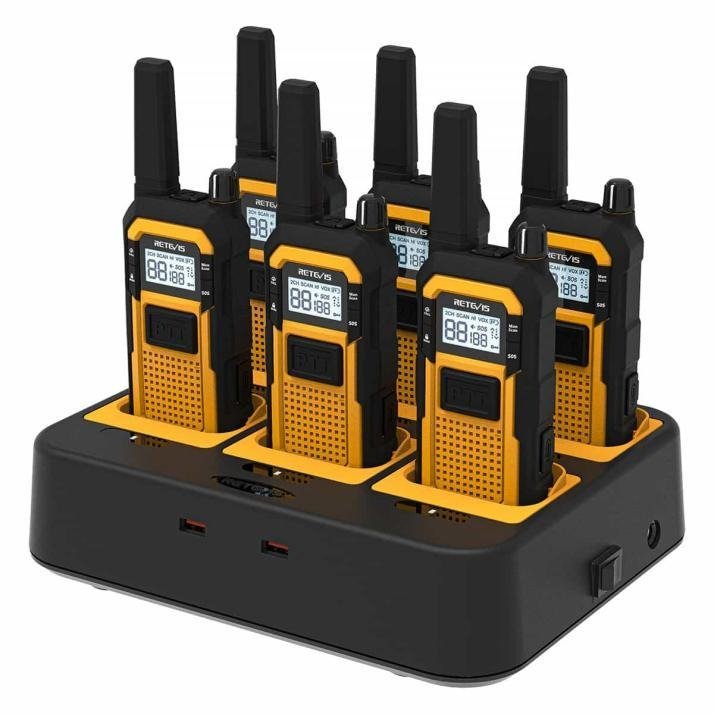
But what does a standard designed for gear that might be airdropped or mounted in a armored vehicle actually mean for a construction foreman, a warehouse manager, or an outdoor adventure guide? We decoded the technical report to translate these brutal lab trials into real-world job site and off-grid reliability.
The Test Chamber as the Ultimate Proving Ground
The official MIL-STD-810H certification, conducted by an accredited lab like GRG Metrology & Test, puts devices through a gauntlet that simulates years of worst-case-scenario abuse in a matter of weeks. For RETEVIS Industrial Two Way Radios, the testing highlights include:
Procedure I – Low-Pressure Operation: The radios functioned normally at an atmospheric pressure equivalent to 15,000 feet of altitude. Real-World Translation: Reliable performance for high-altitude mining, mountain rescue, or aviation ground operations.
Procedure I – Temperature Shock: Units were violently cycled four times between a -40°C (-40°F) deep freeze and a +85°C (185°F) oven in under a minute per transition. Real-World Translation: The radio won’t fail when moved from a freezer warehouse to a sun-baked refinery pipeline or left in a truck overnight in a prairie winter.
Procedure I – Immersion: Submerged in 1 meter of water for 30 minutes. Real-World Translation: It survives being dropped in a mud puddle, used in a torrential downpour, or rinsed off after a dusty shift.
Procedure I & II – Blowing Dust & Sand: Subjected to high-velocity dust and sand storms for multiple hours. Real-World Translation: Internal components stay protected in the abrasive, particulate-filled air of a demolition site, desert oil field, or grain handling facility.
Procedure I & V, VI – Shock and Vibration: Endured repeated 40G and 75G mechanical shock pulses and hours of variable-frequency vibration. Real-World Translation: They withstand the constant jolts inside a heavy machinery cab, the rattling on a forklift, or the impacts from accidental drops on concrete.
“The goal isn’t to create an indestructible brick, but a highly functional tool that is predictably reliable,” explains a RETEVIS engineer. “We design our RETEVIS Industrial Two Way Radios to pass these specific tests because they are a proxy for real-world extremes. If our radios work here, we have high confidence they’ll work for years on a demanding worksite or outdoor expedition.”
Beyond the Battlefield: From Military Spec to “Industrial-Grade” Clarity
This hardware-level toughness is foundational to RETEVIS’s 2026 brand promise: “The Signal Never Drops.” The company is leveraging this engineering credibility to do more than just sell radios; it’s aiming to educate the market. This effort includes the recent release of an “Industrial Wireless Communications Reliability Standard Guide,” a public whitepaper that breaks down device reliability into three clear, actionable tiers.
“Passing MIL-STD-810H is our internal benchmark and the origin of our product’s reliability,” the engineer states. “The public-facing standard is how we help customers choose. Does a campground manager need the same radio as an offshore oil rig mechanic? Probably not. Now there’s a clear framework to understand that difference and select the appropriate RETEVIS Industrial Two Way Radio for the task.”
Why This Matters for Professionals and Outdoor Workers
For businesses, this proven resilience translates directly to lower total cost of ownership (fewer replacements), reduced downtime, and enhanced safety compliance. For expanding user groups like family adventure teams, backcountry hikers, or event organizers, it means trustworthy communication when there’s no cellular signal and conditions get rough.
This move represents a significant shift in a market saturated with buzzwords. By open-sourcing its engineering philosophy and using objectively verified military testing as a baseline, RETEVIS challenges the entire industry to elevate its standards. In environments where a dropped signal means more than static—it could mean a missed safety warning, a delayed critical shipment, or a stranded hiker—this level of transparency and proven performance is becoming essential.
Where to Get the Tested Reliable Comms Gear:
For professionals and prepared individuals seeking this level of verified durability, the RETEVIS RB48 series Industrial Two Way Radios are available for purchase. You can find the latest models and kits on RETEVIS Official Amazon Storefront.
-
 Tech2 years ago
Custom Automotive Parts: Why 5-Axis Machining is the Future
-
Blog1 year ago
Save up to 40% this Prime Day 2025 — Proscenic’s summer-ready vacuums start at just £99
-
 News2 years ago
What Does Senior Home Care Include? A Complete Breakdown
-
 Lifestyle3 years ago
Popular People: Who They Are and Why They Matter
-
 Technology4 years ago
Find incredible discounts on top MagSafe chargers this Black Friday 2023!
-
 Business3 years ago
Navigating the great 1 World of IDs Online: A Step-by-Step Guide on How to Acquire One
-
 Technology4 years ago
The Ultimate Great MPPT: Controllers Optimize Solar Power Production With MPPT Controllers 1
-
 Blog2 years ago
Luxury Denim and Avant-Garde Designs: Discover JUUN.J and Designer Jeans